How does Europe defend itself from cyber attacks today? The measures envisaged by NIS2 and Cyber Resilience Act and the deadlines until 2027.
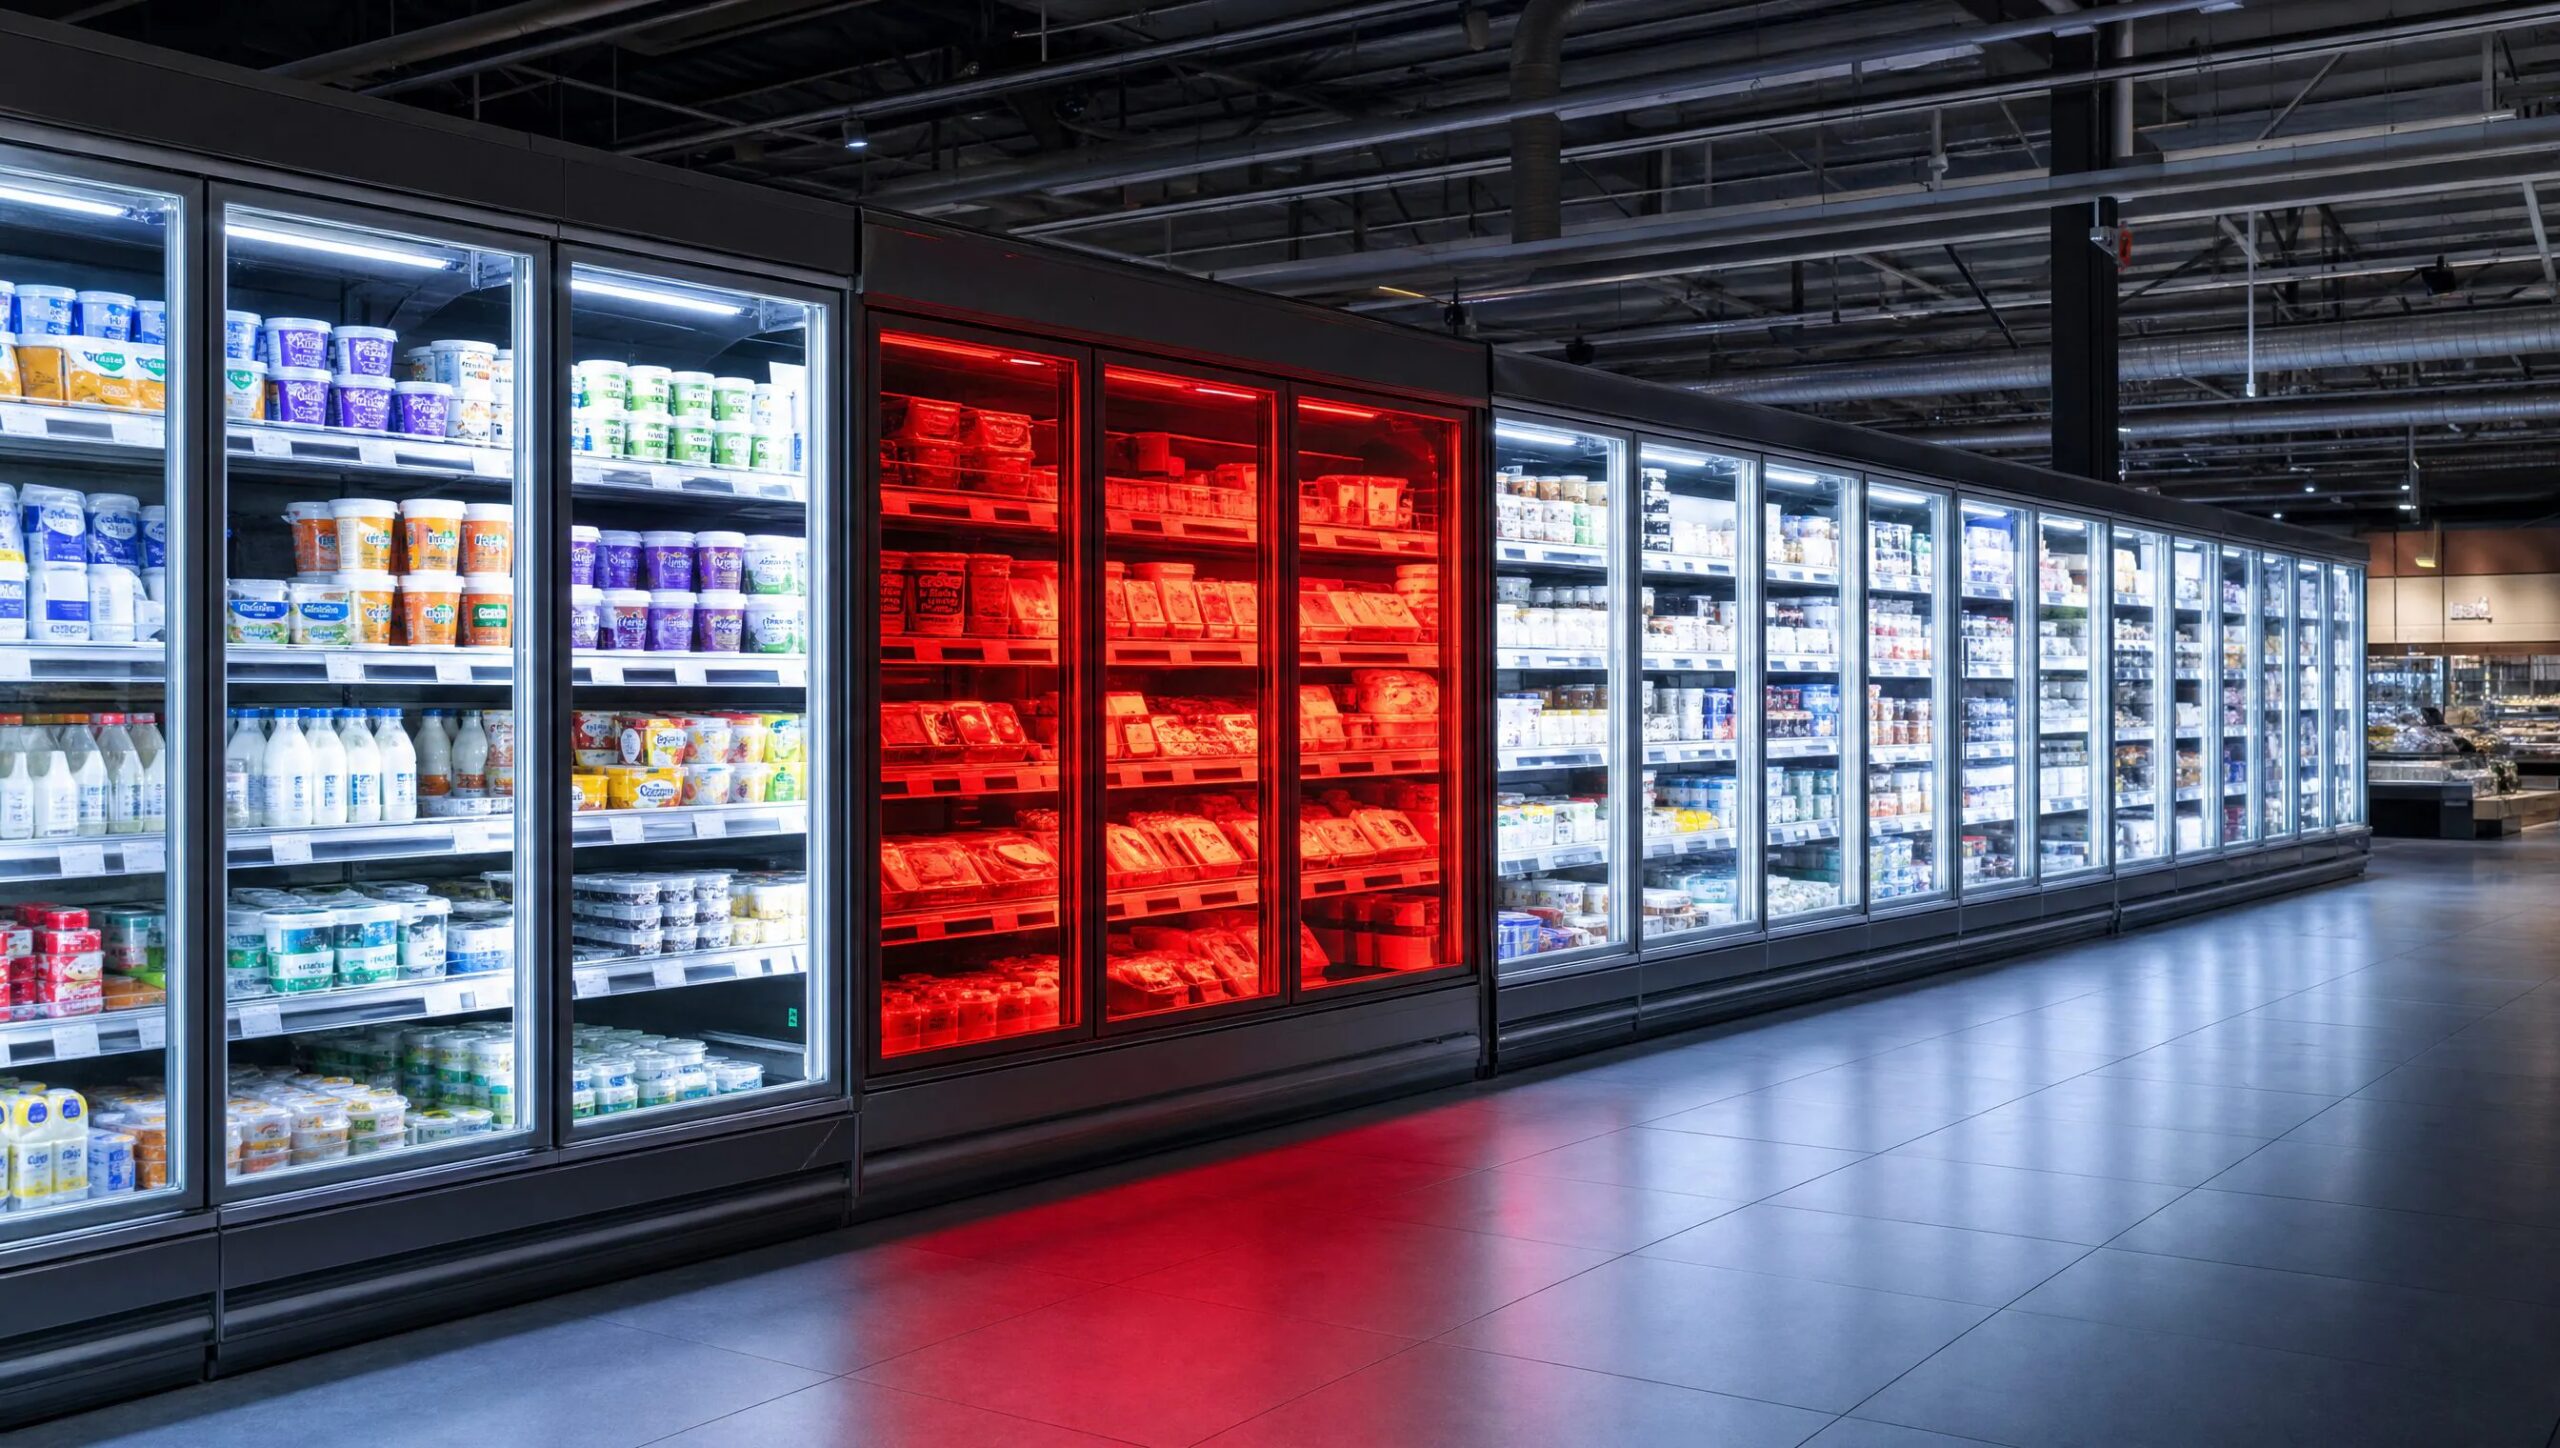
The cyber attacks to the refrigeration systems of European supermarkets, which also involved Italy, brought attention back to the security of devices connected to the Internet. On November 4, 2026, theENISAthe European Union Agency for Cybersecurity, has published a joint communication with other European institutions to invite organizations to take action on potentially exposed systems. The goal is not only to react to the attacks that have already occurred, but above all reduce system vulnerabilities and improve prevention capacitythrough common rules, safer products and greater cooperation between countries.
The case of supermarkets also brings the role of NIS2 directivewhich requires certain companies, including those in certain sectors of the food supply chain, to adopt cybersecurity measures to prevent attacks and limit their consequences. As he explained to us Corrado Giustozzi, professor of cybersecurity at the Campus Bio-Medico University of Rome, the European Union has been working for over ten years to improve the protection of digital systems, through an approach that involves both those who use the technologies and those who produce them. A concrete example of European collaboration comes from the recent accidents to commercial refrigeration systems: the response involved several European structures, including ENISA, Europol, the European Commission and the cyber incident response networks of the Member Statesengaged in monitoring the situation and exchanging information.
Europe’s two strategies to prevent cyber attacks
The European approach to cybersecurity mainly intervenes on two levels:
- the first concerns the organizations that use information systemsfrom companies to essential service operators. The goal is toincrease risk awareness and introduce prevention measures and adequate protection. The. fits in this direction NIS2 directivewhich requires organizations within its scope to take measures to manage cyber risks and report significant incidents to the relevant authorities.
- the second level concerns i device and software manufacturers. With the Cyber Resilience Actwhich came into force in December 2024, the European Union introduced security requirements for products with digital elements, requiring that they be designed with cyber risks in mind and that manufacturers manage vulnerabilities even after marketing.
What the Cyber Resilience Act 2024 regulation provides for connected devices
Among the main European initiatives to prevent cyber attacks, as mentioned, there is the Cyber Resilience Act (CRA)EU Regulation 2024/2847, which came into force on December 10, 2024. The goal is improve product safety that contain digital components, such as computers, internet-connected devices, industrial equipment and software, imposing common European-wide cybersecurity requirements on manufacturers. In Italy, the Council of Ministers approved on 2 October 2026 a draft legislative decree that adapts the national legislation to the CRA.
The principle underlying the regulation is that IT security it must be guaranteed right from the design of the product and maintained even after its sale. Manufacturers will therefore have to evaluate IT risks, design devices with adequate protection measures, avoid marketing products with known and exploitable vulnerabilities without available remedies and intervene on security flaws that are discovered subsequently, even through free updates. They will also have to guarantee a support period generally not less than 5 yearsunless the expected usage life of the product is shorter.
The main provisions of the Cyber Resilience Act will become applicable fromDecember 11, 2027. Already sinceSeptember 11, 2026however, have come into application vulnerability reporting obligations actively exploited and serious IT incidents which compromise the safety of the products concerned, to which Italian companies are already subject. An initial report is expected within 24 hours since they become aware of it and a more detailed notification within 72 hours, through a European platform managed by ENISA. In the event of breaches, consumers can report vulnerabilities and incidents to the CSIRT Italy (national cyber security intervention group).
The legislation establishes that responsibility for IT security it not only falls on companies and citizens who use the devices, but also on those who design, produce and market them, a principle particularly relevant for connected industrial systems. Of course, the regulation does not guarantee that the products placed on the market are completely free of vulnerabilitiesbut imposes requirements to reduce and correct them. Furthermore, not all industrial systems automatically fall under the CRA: applicability depends on the characteristics of the product and any exclusions provided for by the regulation.
The legislation also applies to non-European producers and it was created «precisely to be able to give European citizens the certainty that even non-European products guarantee them the same levels of safety that Europe expects and finds indispensable», explains Giustozzi. The other, easier route would have been to prohibit the sale on European markets of products from manufacturers belonging to “untrusted” countries, as for example the United States has done by declaring the products of some Chinese manufacturers “unwanted”: «but this is an embargo, that is, a political act and Europe has instead chosen to leave the dialogue on a technical level, adopting rigorous but transparent regulations which have the aim of allowing everyone to sell their products in the Union, provided that respect the established safety measures”.
Could cyber attacks on supermarkets have been prevented?
Could the early application of the Cyber Resilience Act have helped prevent the cyber attacks on supermarkets in recent days? «In reality, prevention is entrusted to two rules that cooperate: one has already been in force since 2024the NIS2 Directiveand the other will complete its entry into force next year, namely the CRA. The NIS2 Directive has been in place for a couple of years already imposes on companies and organizations (including those in the large-scale food distribution chain) of raise and verify constantly technical and organizational security measures to protect their business, also considering the risks of an incorrect security posture of their suppliers and service providers such as remote maintenance companies”.
As Giustozzi further explains, the companies affected «have failed in many things already mandatory under NIS2 such as: leaving access to critical components such as refrigerators exposed on the Internet; not having applied the security updates of the producers, already available for some time, who would have remedied the vulnerabilities exploited by the attackers; not having employed safer mechanisms to allow remote maintenance of refrigerators by authorized parties only, such as use of VPN and double-factor authentication; as well as deficiencies in monitoring and errors in the timely detection of anomalous situations”.
The legislation does not necessarily concern all large-scale retail outlets, but for Giustozzi the companies involved probably made errors in the management and configuration of the systems that they should not have made under the NIS2 already in force. The CRA, however, applies to device manufacturersimposing on them among other things safe design criteria by design And by defaultas well as the timely correction of any vulnerabilities as soon as they are discovered. «If it had already been in forceprobably many supermarkets would not have been foundwithout their knowledge, to have vulnerable products at home to attacks like the one that occurred.” The CRA, therefore, will be able to reduce the risk of marketing new insecure products, without however automatically eliminating the vulnerabilities of existing equipment.
What Europe is still missing and what are the risks until 2027
«Europe is unfortunately a complicated place, with 27 countries to reach agreement: and when the issues are particularly critical, as in the case of national security or industrial and productive ecosystems, the differences in vision and jealousies over aspects of national sovereignty become an obstacle in quickly finding shared solutions that gain everyone’s consensus”, explains Corrado Giustozzi.
It is no coincidence, for example, that the GDPR which protects the processing of citizens’ data has been issued as regulationi.e. a rule of the highest rank that applies as is in all Member States without the possibility of modification. NIS And NIS2which concern safety aspects of operators and supply chains that ensure the maintenance of essential services, were instead issued as directivei.e. a lower-ranking rule which involves the step of “transposition” into national legislation by each Member State with extensive “customization” possibilities. The result is still a rather uneven Europe in terms of implementation of what should be a great common defense plan.
Nonetheless, continues Giustozzi, «Europe has nevertheless made an extraordinary journey to secure all the ecosystems of production, services, markets, healthcare and products, both industrial and consumer, designing a complex but coherent puzzle in which each plays its own role, with the aim of raising in a coordinated way the security of the common cyber space and of all the digital services and products essential to the normal functioning of civil society». There cybersecurityit’s not so much a technical problem as a organizational and cultural problemand as such it must be addressed: a bit like what was done for safety in the workplace, the protection of the environment and that of personal data.
It is natural to ask whether December 11, 2027, the date by which the main requirements of the CRA must be applied, is not too far away to respond to the cyber threats of this period. «Whereas the first “cyberstrategy” of the European Unionin which Parliament and the Council took note of the new threat arriving and the need for Member States to prepare common defenses, dates back to 2013 I’d say we’ve come a long way. And, probably, it would not have been possible to go faster than this, because there are so many things to do and they have a huge impact on the functioning of society.”
They have been created since 2013 government prevention and enforcement structures (first the CERTs, then the “cyber arm” of Europol called EC3, then the NIS national contact points and the related transnational rapid communication network, finally the cyber competence center in Bucharest); pan-European exercises have been launched where Member States simulate attacks on critical sectors and verify their collective response capacity; regulations have been passed to increase organizational and technical safety in companies (NIS and NIS2, DORA); regulations have been passed to increase technical safety in digital products and services (CRA, DSA, Machinery Directive).
«Is 2027 far away? Not so much now: and in fact the device manufacturers are even complaining that it is too close, and they fear they won’t have time to adapt!», concludes Giustozzi.